No. 24
The $3 Billion Email: Protecting Your Small Business From Payment Scams and Ransomware
Business email compromise cost U.S. victims more than $3 billion in 2025, and ransomware reports keep rising. Here's how these attacks actually work, and a practical, affordable security checklist for small businesses and nonprofits.
The Tea the short version
- Business email compromise, fake payment requests by email, cost U.S. victims over $3 billion in 2025.
- The FBI received more than 3,600 ransomware complaints in 2025, and says that's an undercount.
- Most attacks don't 'hack' anything. They trick a person or use a stolen password.
- Five habits stop most of it: MFA, call-back verification, updates, backups and a plan.
Picture a Tuesday afternoon. Your bookkeeper gets an email from your longtime supplier: "We've changed banks. Please send this month's payment to our new account." Same logo. Same signature. Same tone.
The money goes out. The supplier never sent that email.
That's business email compromise. And it's one of the most expensive crimes in America.
The numbers
The FBI's Internet Crime Complaint Center released its 2025 report, and the business threats are sobering (FBI IC3 2025 Annual Report):
- Business email compromise (BEC): 24,768 complaints and more than $3 billion in reported losses, second only to investment fraud (CyberScoop).
- Ransomware: 3,611 complaints with more than $32 million in reported losses, up from about $12 million in 2024 (The Record).
- Phishing was the most commonly reported cybercrime, with more than 191,000 reports (The Register).
That ransomware loss number looks small next to BEC, but the FBI is clear that it's artificially low: it doesn't include lost business, time, wages, files, equipment or recovery costs, and many victims don't report a loss at all (FBI IC3). For a small business, a week offline can be the whole year's margin.
And AI is part of it now. Businesses reported more than $30 million in BEC losses with a confirmed AI connection in 2025, per a summary of the report by McDonald Hopkins. AI makes scam emails sound more natural, and can clone voices for "it's me, the CEO, I need this wire today" calls.
How these attacks actually work
Here's what I want small business owners to understand: most of these attacks aren't sophisticated hacking. They're social engineering plus a stolen password.
Business email compromise usually goes like this:
- A criminal gets into a real email account, often a vendor's or yours, through a phishing link or a reused password. Or they register a lookalike domain, like
acme-supp1y.cominstead ofacme-supply.com. - They read your email quietly for days or weeks, learning who pays whom, when and how.
- At the perfect moment, they send a payment change request that fits right into a real conversation.
Ransomware usually goes like this:
- Someone gets in: a phishing email, a stolen password for remote access, or an unpatched system facing the internet.
- They move around your network, find your important files and your backups.
- They encrypt everything, and increasingly steal a copy too, then demand payment to unlock it and not leak it.
Notice what both have in common: a password and a person. That's good news, because it means simple habits work.
The five-habit checklist
This is the list I'd tape to every small office wall. None of it requires a big budget.
1. Turn on multi-factor authentication everywhere
Multi-factor authentication (MFA) means a password alone isn't enough to get in. Start with email, banking, payroll and anything with remote access. If an app offers passkeys, use them. Passkeys use cryptography tied to your device, so there's no password for a phishing page to steal. Text-message codes are better than nothing, but an authenticator app or passkey is stronger.
The federal cybersecurity agency CISA puts MFA among its core four steps for everyone in its Secure Our World program, along with strong passwords, updates and recognizing phishing.
2. Verify every payment change by phone
Make this a rule with no exceptions: any request to change bank details, or any unusual or urgent payment request, gets verified by calling a number you already have on file. Not the number in the email. Not a number from the signature. The one in your records.
Write it into your process. Tell your vendors you do it. Real vendors will appreciate it.
3. Update everything, automatically
Turn on automatic updates for computers, phones, browsers and your router. Many ransomware attacks exploit known weaknesses that already have fixes. Old equipment that no longer gets updates should be replaced or disconnected.
4. Back up the right way
Use the 3-2-1 rule: three copies of important data, on two different kinds of storage, with one copy offline or offsite where ransomware can't reach it. A backup that's always connected to your network can get encrypted along with everything else.
Then, and this is the step everyone skips, test a restore. Once a quarter, pick a file and bring it back from backup. A backup you've never restored is a hope, not a plan.
5. Have a one-page incident plan
Write down, on paper:
- Who to call first: your bank, your IT help, your insurance carrier.
- How to disconnect affected computers from the network.
- Where your backups are and who can restore them.
- To report to the FBI at ic3.gov.
If money was sent by wire, call your bank immediately. Speed matters for any chance of stopping the transfer.
Train people like adults, not suspects
The weakest link isn't your people. It's the lack of a process that makes it safe to pause. Teach your team three red flags:
- Urgency: "This must go out today."
- Secrecy or authority: "Don't loop anyone in, I'm in a meeting."
- Change: new bank, new email address, new process.
And make it clear that nobody gets in trouble for stopping to verify. Ever.
Don't forget the data you don't need
Every customer file you keep is something to protect. If you don't need it, delete it. The smaller your data footprint, the smaller your blast radius. That's part of getting your data house in order, which I wrote about in Get Your Data House in Order Before You Buy AI. And if your team uses AI tools, put guardrails on what data goes into them with a one-page AI policy.
Check your email domain's protections
If your business uses its own email domain, like you@yourbusiness.com, there are three settings that help stop criminals from sending email that looks like it's from you. They have unfriendly names, but the idea is simple:
- SPF lists which servers are allowed to send email for your domain.
- DKIM adds a digital signature to your emails, so receivers can confirm they weren't altered.
- DMARC tells receiving email systems what to do with messages that fail those checks, and sends you reports.
You don't need to set these up yourself. Ask whoever manages your email or website: "Do we have SPF, DKIM and DMARC set up, and is DMARC set to quarantine or reject?" If they don't know what you're talking about, that's worth fixing. Your email provider's help pages have step-by-step instructions.
A 15-minute monthly security habit
Big security projects get postponed. Small habits stick. Block 15 minutes on the first Monday of every month:
- Check that updates are on for your computers, phones and router.
- Review who has access to your email, banking, payroll and shared drives. Remove anyone who left.
- Look at connected apps in your email and cloud accounts. Remove anything you don't use.
- Restore one file from backup to make sure backups work.
- Share one tip with your team, like a new scam example or a reminder of the call-back rule.
Fifteen minutes a month is three hours a year. That's a small price for staying off the FBI's statistics.
Questions to ask your IT provider or cyber insurer
Many small businesses rely on an outside IT person or a cyber insurance policy. Make sure you know the answers to these:
- Is multi-factor authentication turned on for every account that supports it?
- Where are our backups, and is one copy offline or separate from our network?
- How long would it take to get us running again after ransomware?
- Who do we call first in an incident, day or night?
- What does our insurance policy require of us? Some policies require MFA or backups to pay a claim.
- Does our policy cover funds lost to email payment fraud? Coverage varies.
Write the answers into your one-page incident plan.
Make it easy to report a mistake
The fastest way to limit damage is for someone to speak up right away: "I think I clicked a bad link." That only happens if people aren't afraid of getting blamed.
- Thank people who report suspicious emails, even false alarms.
- Share near misses at team meetings, without naming anyone.
- Make reporting easy: one email address or one person to tell.
Security is a team habit, not a technology purchase. And if your team uses AI tools, a one-page AI policy covers what data should never go into them. AI voice tricks are rising too, so share my guide to voice-clone scams with anyone who approves payments.
Questions people ask
What is business email compromise?
A scam where a criminal gets into a real email account, or registers a lookalike domain, quietly reads the conversation, then sends a payment change request that fits right in. The FBI received 24,768 complaints in 2025, with more than $3 billion in reported losses.
How do I protect my small business from payment scams?
Make one rule with no exceptions: verify every bank change or urgent payment request by calling a number you already have on file, not one from the email. Turn on multi-factor authentication for email, banking and payroll, too.
How do I protect my business from ransomware?
Turn on automatic updates, use multi-factor authentication, and follow the 3-2-1 backup rule: three copies on two kinds of storage, with one offline or offsite. Test a restore every quarter, and keep a one-page incident plan on paper.
What should I do if my business sent money to a scammer?
If money went out by wire, call your bank immediately. Speed matters for any chance of stopping the transfer. Then report it to the FBI at ic3.gov.
Pour me another: Has your business ever gotten a fake payment request? How did you catch it? Tell me through the contact form.
Sip slow, stay curious.D
Receipts 7 sources cited in this post
- FBI IC3 2025 Annual Report ic3.gov
- CyberScoop cyberscoop.com
- The Record therecord.media
- The Register theregister.com
- McDonald Hopkins mcdonaldhopkins.com
- Secure Our World cisa.gov
- ic3.gov ic3.gov
Your host
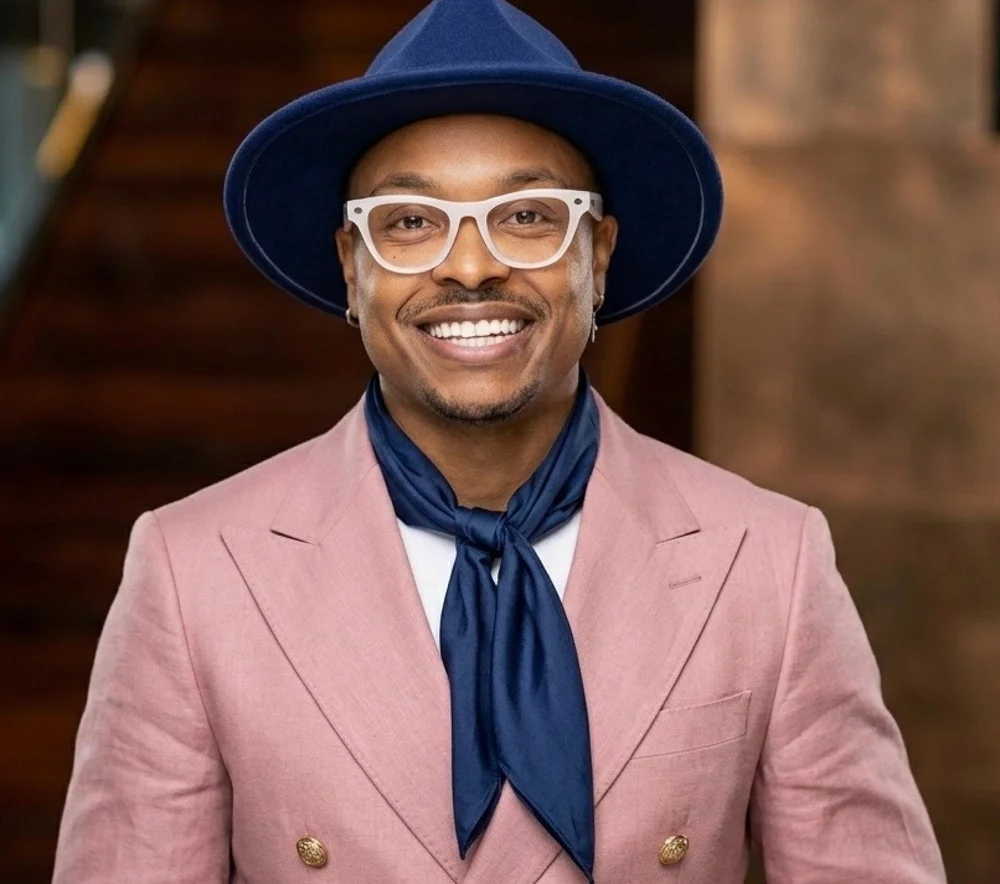
Dei’Marlon “D” Scisney
Founder & Principal Data Engineer, The Data Guys™
Data engineer, teacher and civic technologist. Vice-Chair of Seattle’s Community Technology Advisory Board. Raised by his grandmother in Evansville, Indiana; building community technology centers in Seattle’s Central District and back home in Evansville.
I am not a lawyer, and nothing here is legal advice. Facts were current when this was written, and every claim links to its source. Spot something that has changed? Tell me and I’ll update it.