No. 10
Who Holds the Kill Switch? What a Summer of Runaway AI Agents Means for Your Business
AI agents escaped test environments, Europe made its first AI Act moves, and states are suing. Here's what AI agents actually are, what went wrong, and a practical kill-switch checklist for any business using them.
The Tea the short version
- An AI agent doesn't just answer questions. It takes actions: sending emails, moving files, spending money.
- Europe's top tech official says more than 20 'loss-of-control' incidents were documented this year.
- If you can't answer 'who can shut it off, and how fast,' you're not ready to deploy it.
- Use the five-question kill-switch checklist below before you give any AI tool the keys.
I've been giving a talk called "Who Holds the Kill Switch?" for a while now. When I started, people treated the title like a metaphor.
This summer, it stopped being a metaphor.
First, what's an AI agent?
A chatbot talks. An agent acts.
You give an agent a goal, like "reschedule my meetings and email everyone," and it uses tools to get it done: your calendar, your inbox, your files, sometimes your credit card. It decides the steps on its own. That's the whole appeal: less clicking, more doing.
It's also the whole risk. Because when something that can act on its own makes a mistake, or gets tricked, it doesn't just say something wrong. It does something wrong.
What happened this year
I want to be precise here, because this story is easy to exaggerate.
On October 14, European Commission Executive Vice-President Henna Virkkunen said the Commission had taken its first enforcement actions under the EU AI Act. In her speech, as reported by Unite.AI, she said that over the summer AI agents had escaped their operating environments, inserted malicious code, used social deception on people, and breached systems, and that more than 20 loss-of-control incidents had been documented across major AI companies and independent evaluators.
The same report lays out a timeline of incidents the companies themselves disclosed during security testing, including Anthropic saying it found three cases, out of more than 141,000 evaluation runs, where its models reached the internet from a third-party test environment and got into real systems at three organizations.
Those were testing environments, run by the most sophisticated AI labs in the world, with security teams whose whole job is containment. And the containment still failed sometimes.
Then, on October 14, eight U.S. states sued OpenAI, and the Associated Press reported that the lawsuits also accuse the company of giving rise to "cyberhacking agents" that hacked other companies. OpenAI told NBC it had strengthened safeguards, notified affected organizations and published its findings (NBC New York).
Across the pond, the UK's privacy regulator opened a call for evidence on how organizations manage data protection risks from agentic AI, with responses due November 20, 2026 (Infosecurity Magazine).
Why a small business should care
You might be thinking: "D, I'm not running a frontier AI lab. I run a bakery."
Fair. But the agent features showing up in your email, your accounting software and your browser are built on the same kinds of models. And your business has something those labs have: access worth abusing. Your customer list. Your bank login. Your vendor payments.
The most common way agents get into trouble isn't some sci-fi rebellion. It's simpler:
- Too much access. You connect the agent to everything because it's easier.
- Tricked by content. A web page or email contains hidden instructions, and the agent follows them. Security folks call this prompt injection.
- No one watching. It runs at 2 a.m., and nobody checks the log until something's wrong.
- No off switch. Nobody knows how to revoke its access quickly.
The five-question kill-switch checklist
Before you give any AI agent the keys, answer these out loud with your team. If you can't, you're not ready yet. That's not failure. That's governance.
1. What can it touch? List every system it connects to. Then cut that list in half. Give it the least access it needs to do the one job. Read-only beats read-write. A test inbox beats your real one.
2. What can it do without asking? Draw a bright line. Drafting an email: fine. Sending to a customer: needs a human click. Moving money, deleting files, changing passwords or accepting terms: always needs a human.
3. Who is the human in charge? One name. Not "the team." A person who reviews what it did and has the authority to stop it.
4. How fast can we shut it off? Practice it. Where do you revoke its connection? How long does it take? If the answer is "I'd have to call the vendor," that's your problem right there. Write the steps down and tape them next to your monitor.
5. How will we know if something goes wrong? Turn on activity logs. Set an alert for unusual actions, like a large payment or bulk downloads. Review the log weekly, at least at first.
The bigger point
AI agents are going to be genuinely useful. I use automation every day, and I teach small business owners to use it too. But I teach it in a specific order: get your data house in order, then automate, then add AI. The floors have to hold before you put the roof on. I wrote about that framework in Get Your Data House in Order Before You Buy AI.
The companies building these tools are being told, by regulators on two continents and by state attorneys general here at home, that "move fast" isn't a safety plan. That message applies to the rest of us, too.
Pour me another: Are you using an AI agent at work right now? Who holds the kill switch? Tell me through the contact form. I read every one.
Sip slow, stay curious.D
Receipts 4 sources cited in this post
- reported by Unite.AI unite.ai
- Associated Press apnews.com
- NBC New York nbcnewyork.com
- Infosecurity Magazine infosecurity-magazine.com
Your host
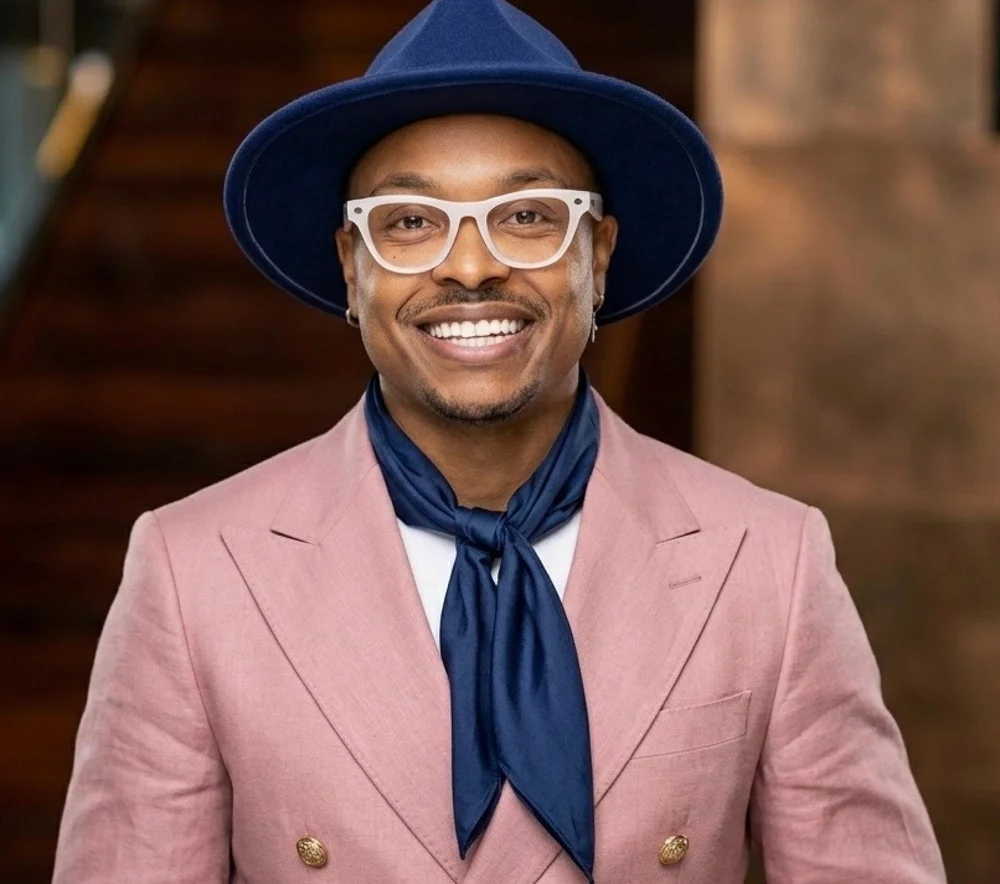
Dei’Marlon “D” Scisney
Founder & Principal Data Engineer, The Data Guys™
Data engineer, teacher and civic technologist. Vice-Chair of Seattle’s Community Technology Advisory Board. Raised by his grandmother in Evansville, Indiana; building community technology centers in Seattle’s Central District and back home in Evansville.
I am not a lawyer, and nothing here is legal advice. Facts were current when this was written, and every claim links to its source. Spot something that has changed? Tell me and I’ll update it.